Účet Kontakt
Váš košík
Doručenie cez DPD a FedEx
Pomoc? Opýtajte sa AI

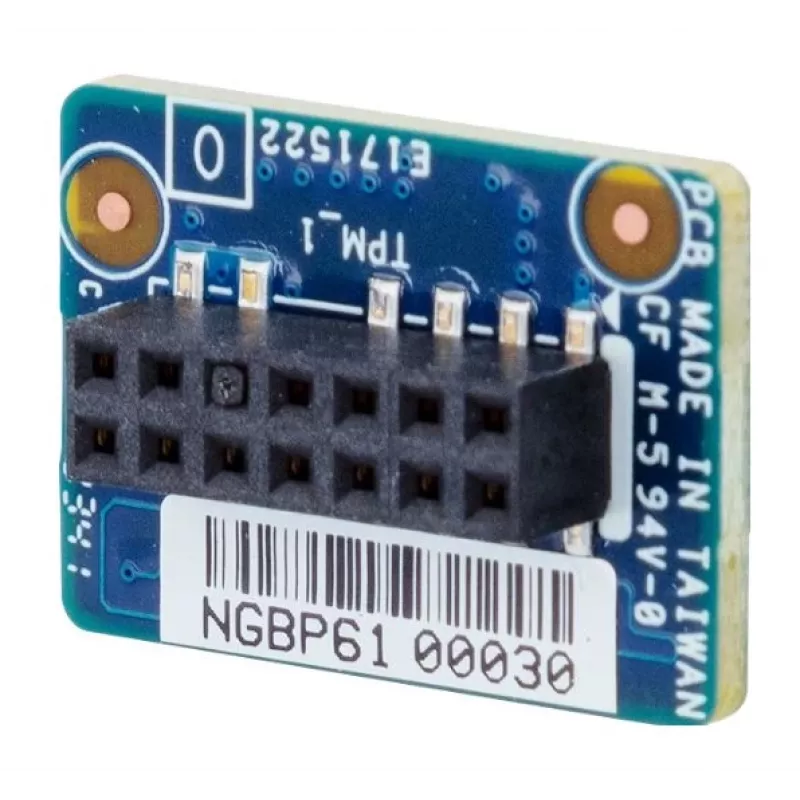
TPM modulová karta GIGABYTE CTM012 2.0 — Trusted Platform Module pre bezpečnosť základnej dosky

TPM modulová karta GIGABYTE CTM012 2.0 — Trusted Platform Module pre bezpečnosť základnej dosky
69,78 €
GIGABYTE TPM Module Card CTM012 2.0 is a Trusted Platform Module designed to provide hardware-based security functions for compatible motherboards. The module offers secure storage for cryptographic keys, supports platform integrity verification and BIOS/boot protection, and enables operating system... Čítať viac
Sklad 125 Kód 2525021 Značka GIGABYTE Model 9CTM012NR-00 Záruka 2 roky

Doprava a vrátenie tovaru

Predpokladané doručenie streda, októbra 28
O stave zásielky Vás budeme priebežne informovať prostredníctvom nášho podrobného systému sledovania zásielok
Možnosti platby
Platobná kartaVisaMastercardPayPalApple PayGoogle PayBankový prevod

GIGABYTE TPM Module Card CTM012 2.0 is a Trusted Platform Module designed to provide hardware-based security functions for compatible motherboards. The module offers secure storage for cryptographic keys, supports platform integrity verification and BIOS/boot protection, and enables operating system features and applications that require TPM. It is a compact add-on card that integrates with supported GIGABYTE motherboards to extend system security capabilities without changing existing software.

Advantages

The TPM module delivers a hardware root of trust for cryptographic operations and key storage, reducing reliance on software-only protections. It supports secure boot and platform attestation to help verify system integrity during startup. The module is designed for straightforward integration with compatible motherboards, occupying minimal board space while offering persistent, tamper-resistant storage for encryption keys and certificates. Its presence enables native OS security features and enterprise management workflows that depend on TPM functionality.

Suitable for

  • Enabling operating system features that require TPM (disk encryption, credential protection)
  • Secure boot and BIOS/firmware integrity verification
  • Hardware-backed key storage for encryption and authentication
  • Enterprise and workstation systems that need platform attestation and enhanced security

Key specifications

  • TPM version: 2.0 compliant specification
  • Form factor: compact module card for compatible motherboard TPM header
  • Functionality: secure cryptographic key storage, platform integrity verification, secure boot support
  • Compatibility: designed for use with compatible GIGABYTE motherboards supporting external TPM modules
  • Data persistence: tamper-resistant non-volatile storage for keys and credentials

How to use

Install the TPM module into the dedicated TPM header on a compatible motherboard following the motherboard manufacturer’s instructions. After physical installation, enable TPM support in the motherboard BIOS/UEFI and update firmware if required. Once the system recognizes the module, enable the desired operating system security features such as disk encryption (BitLocker or equivalent), secure boot, or credential protection. Manage TPM keys and policies using the OS or enterprise management tools according to your security requirements.

Recommendations

Confirm motherboard compatibility and BIOS/UEFI support before installation. Back up critical data and record TPM ownership/recovery keys when enabling encryption features. Keep motherboard firmware up to date and follow vendor guidance for secure configuration and key management.

Hlavné vlastnosti
  • Enabling operating system features that require TPM (disk encryption, credential protection)
  • Secure boot and BIOS/firmware integrity verification
  • Hardware-backed key storage for encryption and authentication
  • Enterprise and workstation systems that need platform attestation and enhanced security
  • TPM version: 2.0 compliant specification
  • Form factor: compact module card for compatible motherboard TPM header
  • Functionality: secure cryptographic key storage, platform integrity verification, secure boot support
  • Compatibility: designed for use with compatible GIGABYTE motherboards supporting external TPM modules
  • Data persistence: tamper-resistant non-volatile storage for keys and credentials
Vývoj ceny za posledných 6 mesiacov
TPM modulová karta GIGABYTE CTM012 2.0 — Trusted Platform Module pre bezpečnosť základnej dosky
Aktuálna
69,78 €
Najnižšia
39,89 €
Najvyššia
83,64 €
Zmena za 24 h
+0,74 €   +1%
Týždeň
+29,46 €   +73%
Mesiac
-13,10 €   -16%
Dobrý deň, som AI asistent DistriNode. Pomôžem Vám nájsť produkty, porovnať možnosti, vytvoriť cenovú ponuku v PDF alebo otvoriť požiadavku na podporu.